Authentic Passport Data Alone Cannot Rule Out a Cloned Chip
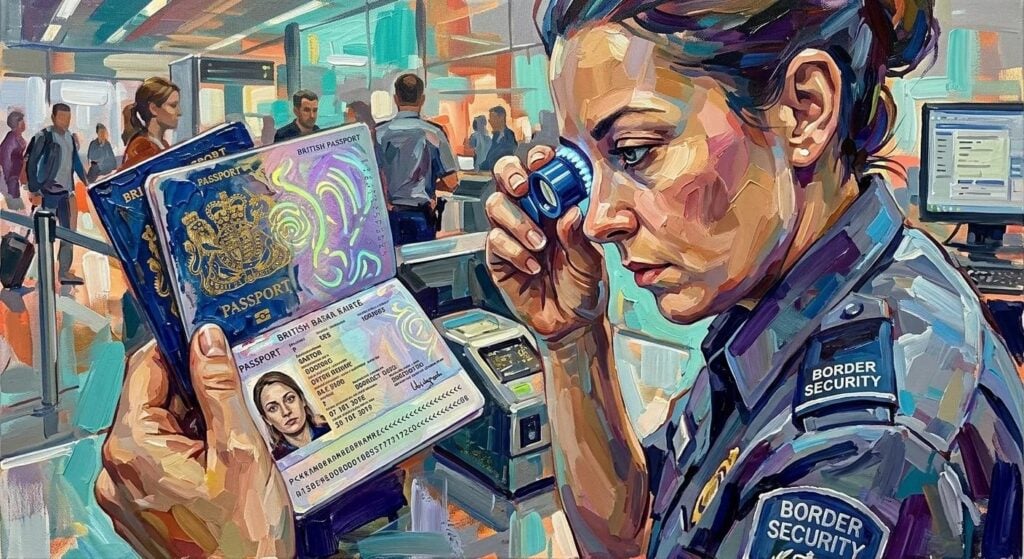
Copied information can retain a valid digital signature, making additional chip authentication an important security safeguard.
WASHINGTON, DC, October 15, 2026 — Electronic passport validation can confirm that protected identity information remains unchanged and was signed within a trusted issuing framework, yet that result alone does not always establish that the physical contactless chip carrying those data is the original chip placed inside the legitimate passport during government personalization.
This distinction matters because copied electronic information can preserve the original passport’s digital signature and data integrity, so authorities may need additional mechanisms, such as Active Authentication or Chip Authentication, for stronger evidence that the electronic component itself has not been substituted or cloned.
Passive Authentication Protects Data Integrity
The first major electronic check is usually passive authentication, which verifies the digital signature protecting the passport chip’s stored information and confirms that the data remain consistent with what the issuing authority originally signed during legitimate document production.
The International Civil Aviation Organization’s ePassport validation framework explains that passive authentication confirms the authenticity and integrity of protected passport information, while additional mechanisms can determine whether the electronic information comes from a genuine chip rather than a copied substitute.
A Valid Signature Can Survive Data Copying
A digital signature protects the relationship between the stored information and the issuing authority, but copying that information exactly can preserve the original signature because a simple duplication process doesn’t necessarily change anything inside the protected data.
In such a scenario, a reader performing only passive authentication could determine that the copied information remains genuine and unaltered, even though the inspection system has not yet established that the chip physically presenting those data is the original secure component.
Authentic Data and an Authentic Chip Are Different Questions
This difference reflects a broader principle in electronic document security: determining whether information is genuine is not always the same as determining whether the hardware presenting that information is the original secure device associated with the physical passport.
A cloned chip can theoretically present accurate biographical information, a genuine facial image, and an unchanged digital signature, yet still fail stronger electronic checks designed to verify possession of cryptographic secrets that were never intended to leave the original secure chip.
Active Authentication Was Designed to Address Cloning
Active Authentication provides one method for checking whether the contactless chip holds a private cryptographic key associated with the genuine passport, rather than merely containing copied electronic files from another legitimate document.
According to ICAO Doc 9303, the inspection system can perform a challenge-response exchange using authentication keys stored within the passport, allowing the reader to assess whether the Document Security Object belongs to the physical document and whether the chip is genuine.
The Private Key Is the Critical Difference
This approach depends on the private authentication key remaining securely stored inside the original chip and unavailable for ordinary copying, so duplicated data alone should not provide everything needed to answer a fresh cryptographic challenge.
The corresponding public information can remain readable and protected within the passport data structure, while the private key performs the secret cryptographic operation that demonstrates the chip possesses a capability associated with the legitimate document.
Challenge-Response Creates Fresh Evidence
During Active Authentication, the inspection system sends a fresh challenge to the chip rather than relying entirely upon static information previously written during passport issuance, requiring the electronic component to calculate a valid response using its protected private key.
A cloned storage device carrying copied passport files may reproduce static information accurately, yet it should be unable to generate the correct cryptographic response unless the attacker also obtained the secret key required by the authentication protocol.
This dynamic exchange therefore provides evidence that differs fundamentally from passive authentication because the reader tests what the chip can do rather than merely evaluating information the chip stores.
Chip Authentication Provides a More Advanced Mechanism
Chip Authentication offers another approach by using a cryptographic key-agreement protocol that authenticates the passport chip while also creating strong session keys for subsequent protected communication between the electronic document and inspection system.
ICAO describes Chip Authentication as a mechanism providing unilateral authentication of the electronic travel-document chip while establishing secure communication, and the relevant private key must remain securely stored within the passport chip’s protected memory.
Cloning Signed Data Does Not Clone Secret Capabilities
The distinction between copied information and copied cryptographic capability is central to understanding why chip authentication matters, because a perfect duplicate of public or signed passport data does not necessarily reproduce the protected secrets held inside secure hardware.
A genuine chip can therefore demonstrate possession of a secret key during an interactive protocol, while a simple clone containing only copied files may reproduce the passport’s visible electronic contents but cannot perform the required cryptographic operation.
Digital Signatures Still Remain Essential
The possibility of cloning does not reduce the importance of passive authentication, because digital signatures still provide the primary protection against unauthorized modification of the biographical and biometric information stored within the electronic passport.
Without that integrity check, a reader would have much less confidence that names, dates, document numbers, or facial images remained unchanged from legitimate issuance, even if the physical chip itself demonstrated some form of hardware authenticity.
The strongest electronic verification therefore combines data-integrity checks with chip-authentication mechanisms when the passport supports them and the receiving inspection system is equipped to perform those procedures.
Not Every Electronic Passport Supports the Same Anti-Cloning Mechanism
Electronic passports have evolved through several technical generations, so some documents support Active Authentication, others support Chip Authentication, and still others may use different combinations of security mechanisms depending on the issuing authority and passport generation.
ICAO states that issuing authorities may implement additional protections against chip substitution, including Active Authentication, Chip Authentication, or PACE with Chip Authentication Mapping, while passive authentication remains the minimum validation process required for electronic passport data.
Older Passports Can Still Be Legitimate
A passport that does not support the newest chip-authentication mechanism should not automatically be regarded as fraudulent, because legitimate documents can remain valid for years after governments introduce stronger electronic security in newer generations.
Border systems must therefore identify which security mechanisms the presented passport legitimately supports and interpret the available results according to that document’s technical generation rather than expecting every electronic passport to implement identical capabilities.
Passive Authentication and Chip Authentication Complement Each Other
Passive authentication asks whether the stored information remains authentic and unchanged, while chip authentication asks whether the electronic component presenting that information possesses the cryptographic capability expected from the original secure passport chip.
These two questions are closely related but not interchangeable, so a system that performs both provides stronger evidence than one that only verifies the static digital signature protecting copied passport information.
Physical Passport Examination Still Matters
Even successful chip authentication cannot establish that every physical component of the passport booklet remains untouched, because electronic protocols do not independently examine stitching, page substitution, holograms, laser engraving, watermarks, microprinting, or other physical characteristics.
A sophisticated border inspection therefore compares authenticated electronic information with the visible data page and broader booklet, creating additional opportunities to identify situations where a legitimate chip has been moved, the physical passport has been altered, or other inconsistencies remain.
The Physical and Electronic Document Should Belong Together
Active Authentication is specifically designed to help establish a relationship between the protected electronic component and the physical travel document, rather than merely confirming that individually copied data retain a valid government signature.
ICAO’s current specifications describe successful Active Authentication as evidence that the Document Security Object belongs to the physical passport, the contactless chip is genuine, and the chip and physical document belong together.
A Genuine Chip Can Still Exist in the Wrong Context
Even when a chip is genuine, border authorities may still need to determine whether it remains in the legitimate document to which it was originally associated, especially when physical inspection reveals unusual construction or evidence of booklet manipulation.
Electronic authentication is stronger when inspectors compare chip results with the machine-readable zone, visible identity information, physical materials, and document construction, rather than treating the electronic component as an isolated credential.
Facial Comparison Addresses Yet Another Question
Once authorities establish confidence in the passport data and electronic component, they can compare the stored facial image with the live traveler, addressing whether the person presenting the document corresponds with the identity protected within the passport.
This biometric step does not duplicate chip authentication because an impostor could still present a genuine chip, just as a strong facial resemblance cannot prove the electronic document is technically authentic.
Current Passport Status Also Requires Separate Checks
A passport containing genuine data on a genuine chip can still become invalid if the issuing authority later cancels, revokes, or reports the document lost or stolen, meaning cryptographic authenticity does not automatically establish current travel validity.
Government status databases therefore contribute another independent layer by describing events occurring after issuance that neither passive authentication nor chip authentication was designed to detect.
Consumer Applications May Not Perform Every Check
Smartphone applications can read electronic passports and some can perform passive authentication, but their ability to conduct Active Authentication, Chip Authentication, certificate validation, or other advanced procedures varies considerably according to software design and supported document generations.
A consumer application reporting valid signed data should therefore be interpreted based on the specific checks it actually performed, rather than automatically treated as proof that the chip itself was tested against cloning or substitution.
A Green Authentication Result Needs Precise Meaning
The word authenticated can describe several technical outcomes, so it matters whether software verified only the digital signature, evaluated certificate trust, performed anti-cloning authentication, or completed several electronic checks together.
Without that distinction, users may incorrectly assume a successful passive-authentication result proves every aspect of the electronic passport, even though ICAO treats anti-cloning checks as separate mechanisms when the chip supports them.
Anti-Cloning Checks Depend on Secure Hardware
Chip-authentication mechanisms derive much of their value from the assumption that sensitive private keys remain protected inside tamper-resistant electronic hardware and cannot simply be extracted alongside ordinary readable passport information.
If secret keys were easily exportable, a sophisticated attacker could potentially reproduce both the data and the cryptographic capability required for authentication, undermining the distinction between the original component and a copied device.
Secure chip design therefore complements cryptographic protocol design because mathematical authentication remains effective only when the underlying hardware protects the secret information the protocol depends on.
Cloning Is Different From Altering Data
Electronic cloning and electronic tampering pose different threats: cloning attempts to reproduce legitimate information, while data tampering attempts to modify protected information and still make the altered content appear trustworthy.
Digital signatures are particularly effective against unauthorized data modification, while Active Authentication and Chip Authentication strengthen defenses against substitution or cloning of otherwise valid signed information.
This division of responsibilities shows why electronic passport security uses several cryptographic mechanisms instead of relying on one universal check for every type of attack.
The Inspection System Must Support the Available Mechanism
A passport can support an advanced chip-authentication feature, but a particular reader may not use it because the inspection system lacks the compatible software, certificates, cryptographic support, or operational procedures required for that mechanism.
ICAO therefore recommends that border systems interpret electronic validation through defined procedures, allowing receiving states to determine which supported checks to perform and how to present results to border officers.
International Verification Depends on Shared Standards
Electronic passports cross borders constantly, meaning anti-cloning technologies need standardized structures that compatible foreign readers can recognize without requiring access to the issuing government’s private manufacturing systems.
ICAO Doc 9303 provides that common technical framework, allowing governments to implement secure electronic features while giving receiving authorities specifications for determining how supported authentication mechanisms should operate during international document inspection.
A Failure Does Not Automatically Identify the Cause
When an anti-cloning check fails, authorities still need context before deciding whether the result reflects an actual cloned chip, a damaged document, incompatible equipment, software limitations, communication problems, or another technical condition.
Professional systems therefore use electronic authentication as evidence within a larger inspection process rather than assuming that one failed cryptographic interaction automatically proves the exact type of fraud involved.
Successful Anti-Cloning Authentication Also Has Limits
A successful Active Authentication or Chip Authentication result strengthens confidence in the electronic component, yet it does not independently establish current passport validity, legitimate possession, immigration eligibility, or the integrity of every physical page in the booklet.
Those questions require facial comparison, physical inspection, government database checks, and other procedures that serve purposes separate from confirming whether the chip has the expected cryptographic capabilities.
Cloned Data Can Look Completely Authentic
The challenge of cloning is that the copied information may be genuinely signed and internally correct because the attacker reproduces legitimate data rather than changing the protected identity record.
A system examining only static signed information can therefore encounter a technically valid signature even though the same electronic contents exist on a device other than the original secure chip associated with the legitimate passport.
This is why stronger systems ask not only whether the data are authentic but also whether the electronic component can demonstrate possession of protected cryptographic secrets expected from the genuine document.
Authentication Works Best as a Sequence of Independent Questions
A robust inspection process can ask whether the chip is accessible, whether the stored information remains digitally signed and unchanged, whether the physical chip is genuine, whether the visible document matches the electronic information, and whether the traveler matches the protected portrait.
Each question addresses a different weakness, making the combined process significantly stronger than a single successful electronic result that answers only one part of the broader authenticity problem.
Modern Passport Security Separates Data From Hardware Trust
The evolution of electronic passports illustrates an important security principle: trust in information and trust in the device carrying that information are deliberately evaluated through different cryptographic mechanisms whenever the supported technology permits such separation.
Through Amicus International Consulting’s passport security resource, readers can see how chip authentication fits alongside digital signatures, physical document safeguards, biometric comparison, and international certificate infrastructure in modern passport verification.
Valid Signed Data Are Important, but They Are Not the Entire Story
Authentic passport data provide strong evidence because a valid digital signature can show that protected information remains unchanged from legitimate issuance, but verification does not necessarily establish that the chip presenting that data is the original secure electronic component.
Active Authentication, Chip Authentication, and related mechanisms strengthen the process by testing cryptographic capabilities associated with the chip itself, helping inspection systems distinguish between legitimately signed information and a copied electronic representation when the passport generation supports those safeguards.
Modern electronic passport verification is strongest when data integrity, chip authenticity, physical document consistency, biometric holder verification, and current government status all support the same conclusion, rather than relying on a single successful cryptographic result.